CISA KEV
15 articles
Advertisement
Articles15
 Unit 42 Links Fortinet Path-Traversal Bug to Memory-Only FortiGate Implant in Telecom Intrusion
Attackers stole the configurations of 500+ firewalls from one FortiManager, then planted PEERSTITCH. CISA adde...
KE
20 Oct
 A Third Citrix NetScaler Flaw Hit Appliances That Had Installed Last Week's Emergency Fix
CVE-2026-88779 affects boxes that use SAML sign-in. Citrix calls it a crash; a researcher found malware runnin...
KE
5 Oct
 Fortinet's Email Gateway Is Under Attack, and No Fixed Version Is Out Yet
A critical FortiMail flaw lets anyone who can reach it over the network write files and run code. Until update...
KE
2 Oct
 A Pixel Modem Flaw Needs No Tap, and CISA Gave Three Days
The modem is a separate computer that answers to the mobile network, not to you. Nothing has to be opened, cli...
PR
19 Sep
 A 7.8 Flaw in Acronis Backup Plugins Is Being Exploited Now
Local privilege escalation rarely alarms anyone. On shared hosting, where every customer already has a low-pri...
KE
18 Sep
 CISA Added Five Exploited Flaws, All in Software That Manages Other Machines
JFrog Artifactory builds your software, ConnectWise ScreenConnect reaches into your machines and MikroTik Rout...
KE
13 Sep
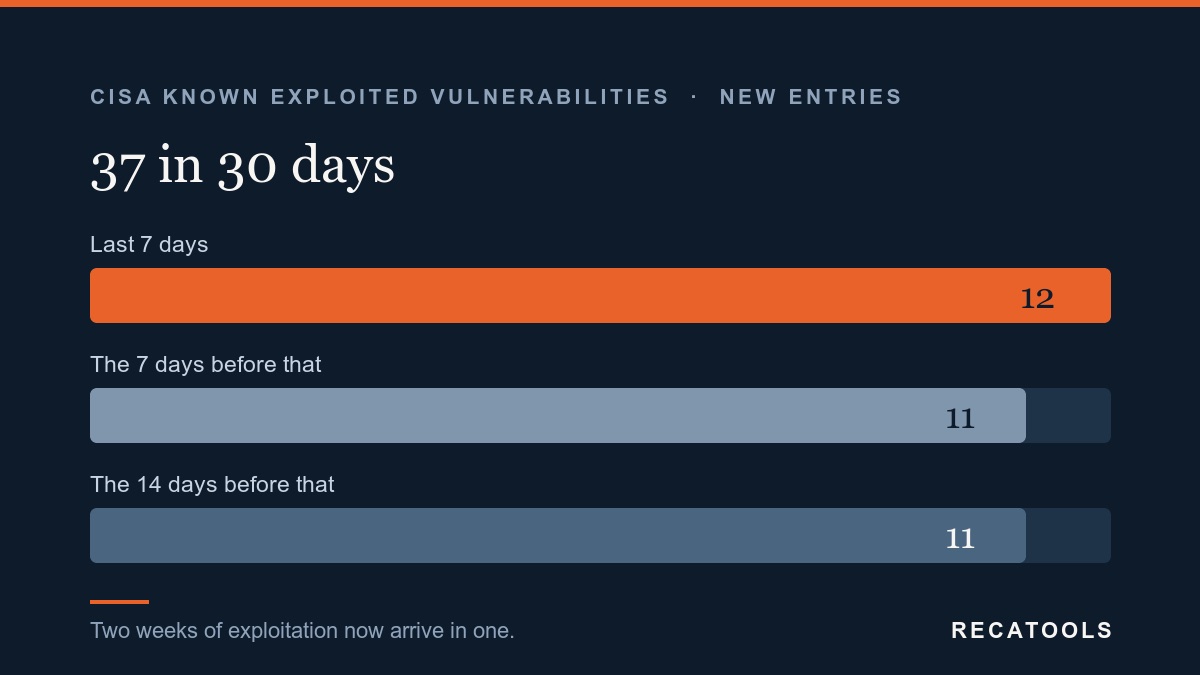 CISA Has Logged 37 Newly Exploited Flaws in 30 Days
CISA's exploited-vulnerability catalogue has taken 37 new entries in 30 days, including this week's Citrix Net...
KE
11 Sep
 Chrome's Sixth Zero-Day of 2026, and Browser Zero-Days Keep Falling
CVE-2026-85046 is a V8 type confusion patched in Chrome 152 with a CISA deadline of 18 September. Across all b...
KE
7 Sep
 CISA Added Seven Exploited Flaws. Five Due in Three Days, Two in Fourteen.
Five carry a three-day federal clock, two carry fourteen days, in a single batch. Three of the seven sit in AI...
PR
4 Sep
 Exploited Gitea Flaw Hinges on Repository Write Access
CVE-2026-60004 lets anyone who can push to a repo plant a Git hook and run shell commands as the service accou...
KE
27 Aug
 A Password Was Built Into Cisco's Firewall Manager. It Is Being Exploited, and Agencies Had Three Days to Fix It
CVE-2026-20316 scores 5.3 — a medium. CISA still gave federal agencies three days and told them to check for c...
CY
1 Aug
 Adobe ColdFusion CVE-2026-48282: A Perfect-Score Path-Traversal Flaw CISA Says Is Being Exploited
CISA added a maximum-severity Adobe ColdFusion path-traversal flaw to its exploited-vulnerabilities catalog on...
CY
11 Jul
 SharePoint RCE CVE-2026-45659 Added to CISA KEV: A 'Less Likely' May Patch Is Now Actively Exploited
CISA added CVE-2026-45659, a CVSS 8.8 deserialization remote-code-execution flaw in on-premises Microsoft Shar...
CY
6 Jul
 SolarWinds Serv-U Enters CISA KEV After Active Exploitation Warning
SolarWinds Serv-U CVE-2026-28318 is now in CISA’s Known Exploited Vulnerabilities catalogue after a June 2026...
CY
7 Jun
 Microsoft Exchange OWA Zero-Day CVE-2026-42897 Actively Exploited With No Permanent Patch
Microsoft confirmed active exploitation of CVE-2026-42897, an XSS flaw in Exchange's Outlook Web Access, on 14...
CY
2 Jun
Advertisement