14 OCT 2026 — Attackers took control of refrigeration systems in hundreds of French supermarkets overnight into Monday 12 October, pushing fridge temperatures as high as 50°C, spoiling stock and in some stores causing fires. France's national cybersecurity agency, ANSSI, says the compromised devices were remote management controllers made by Danfoss, Copeland and its Dixell brand, and that the campaign is probably still running.
So far, no one has claimed the operation and no ransom demand has surfaced. The common thread in the accounts is unglamorous: a controller left reachable from the internet and running old firmware.
What happened in the stores
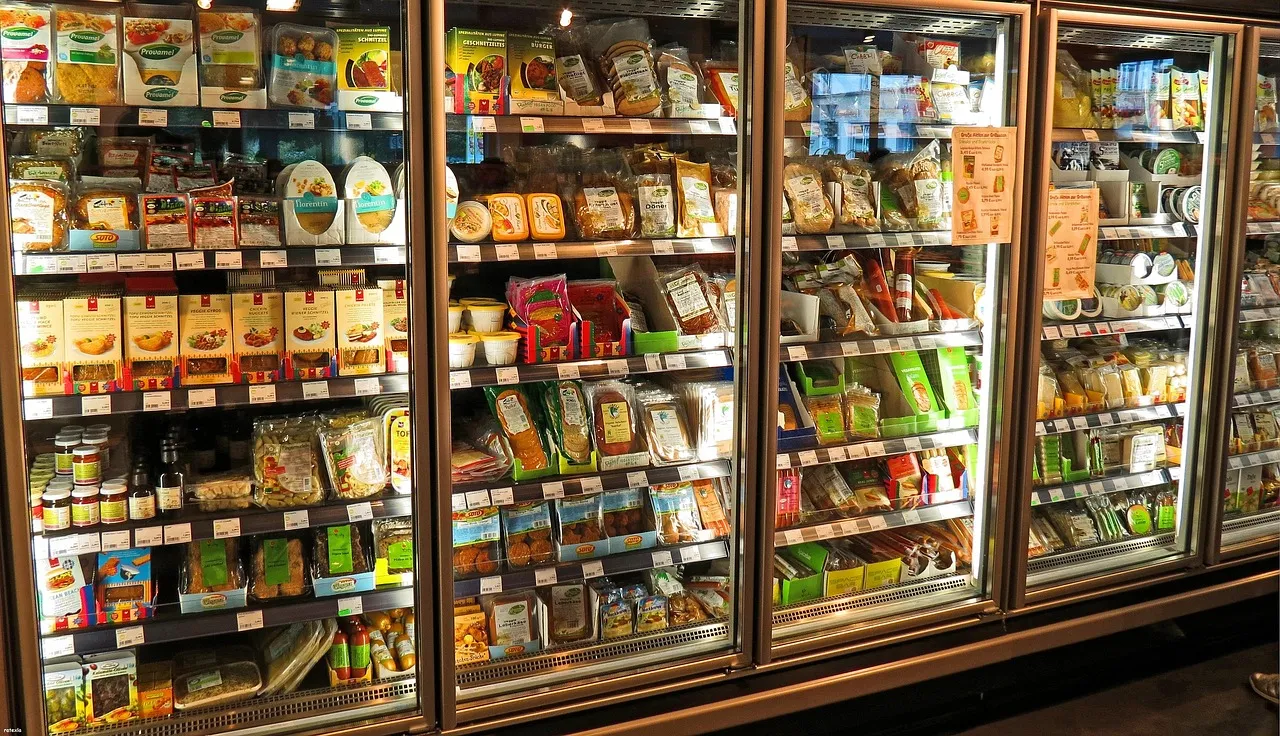
The Paris prosecutor's office described a large-scale attack "affecting connected refrigerators in several major food retailers across France", with "food losses and fires", Reuters reported. Les Mousquetaires, which owns Intermarché, said about 150 of its stores were hit, with fridges held at 50°C for six hours, and that it threw the food away. Coopérative U's chief executive, Dominique Schelcher, called the targeting of equipment that keeps fresh food safe "of extreme gravity" and "unprecedented".
By the next day Reuters counted at least 350 affected supermarkets across chains including Carrefour, Monoprix, Intermarché and Coopérative U. Prime Minister Sébastien Lecornu asked ANSSI to investigate, and a person in his office said France was coordinating with European counterparts in case other countries were affected.
What France's cyber agency says
CERT-FR, ANSSI's response team, issued an alert on 12 October saying it was aware of "numerous compromises" of Danfoss AK-SM and AK-SC refrigeration controllers. On 13 October it added Copeland XWEB and Dixell XWEB devices. Asked by Reuters, a Copeland spokesperson declined to confirm that.
The alert's first point is blunt: exposing a management interface directly to the internet is contrary to good practice. It warns that attack campaigns against these devices are probably still under way, and that a device past its end of life left online is very likely to be compromised. Even a factory reset is not enough for an unsupported unit, CERT-FR says, because the reset removes the attacker's foothold but leaves the device just as vulnerable as before.
Old firmware, and known weaknesses
Danfoss told Reuters that many of the affected units "reached end of life and no longer receive software or security updates", or were running outdated firmware, and that it had long advised customers to update and to migrate legacy systems. How the attackers got in has not been disclosed.
Serious weaknesses in one of these products have been public for two months. On 9 August, Claroty's Team82 published research on the Danfoss AK-SM 800A system manager: a hidden "code-of-the-day" login that could bypass authentication, plus a command injection that led to remote code execution. Danfoss fixed both in new firmware, but nobody has yet said that these were the flaws used in France.
Vandalism, or something else
The lack of a claim or a ransom has puzzled investigators, according to a source quoted by Reuters. Ken Munro of Pen Test Partners called it "basic cyber hygiene" and said the attack could easily be "kids messing around". "If this was a nation state, why affect only a subset of French fridges?" he asked. No one has tied the incident to a state. Last month President Emmanuel Macron ordered measures to protect French critical infrastructure from Russian "hybrid attacks", Reuters noted.
The Dutch retailer Ahold Delhaize took several systems offline on 12 October over a separate "security issue". Reuters said it was not clear whether the two were linked, and nothing published since has shown that they were.
What operators should do now
The same controllers run cold rooms and supermarkets in many markets, so CERT-FR's checklist applies beyond France. Take every unit off public IP addresses. Before you cut a refrigeration contractor's remote data feed, check the insurance terms. Review the whole configuration, especially defrost schedules, since forced defrosting was one of the reported effects. Restore remote access only through a VPN or a protected network, update firmware, and change default passwords. In an emergency, filtering contractor IP addresses at the firewall will do, but the agency says it should not be treated as permanent.
Reuters' Shodan count suggests the job is far from done. French scanning firm Onyphe said only a small minority of the exposed Danfoss interfaces appeared to run the latest software.
View author profile → · Editorial policy